CyberTix AI: AI Runtime Security for Enterprise AI
Secure the AI you build. Defend against the AI used against you. One runtime backbone.
Part of the Cygeniq Runtime AI Trust Platform: Defend with AI.
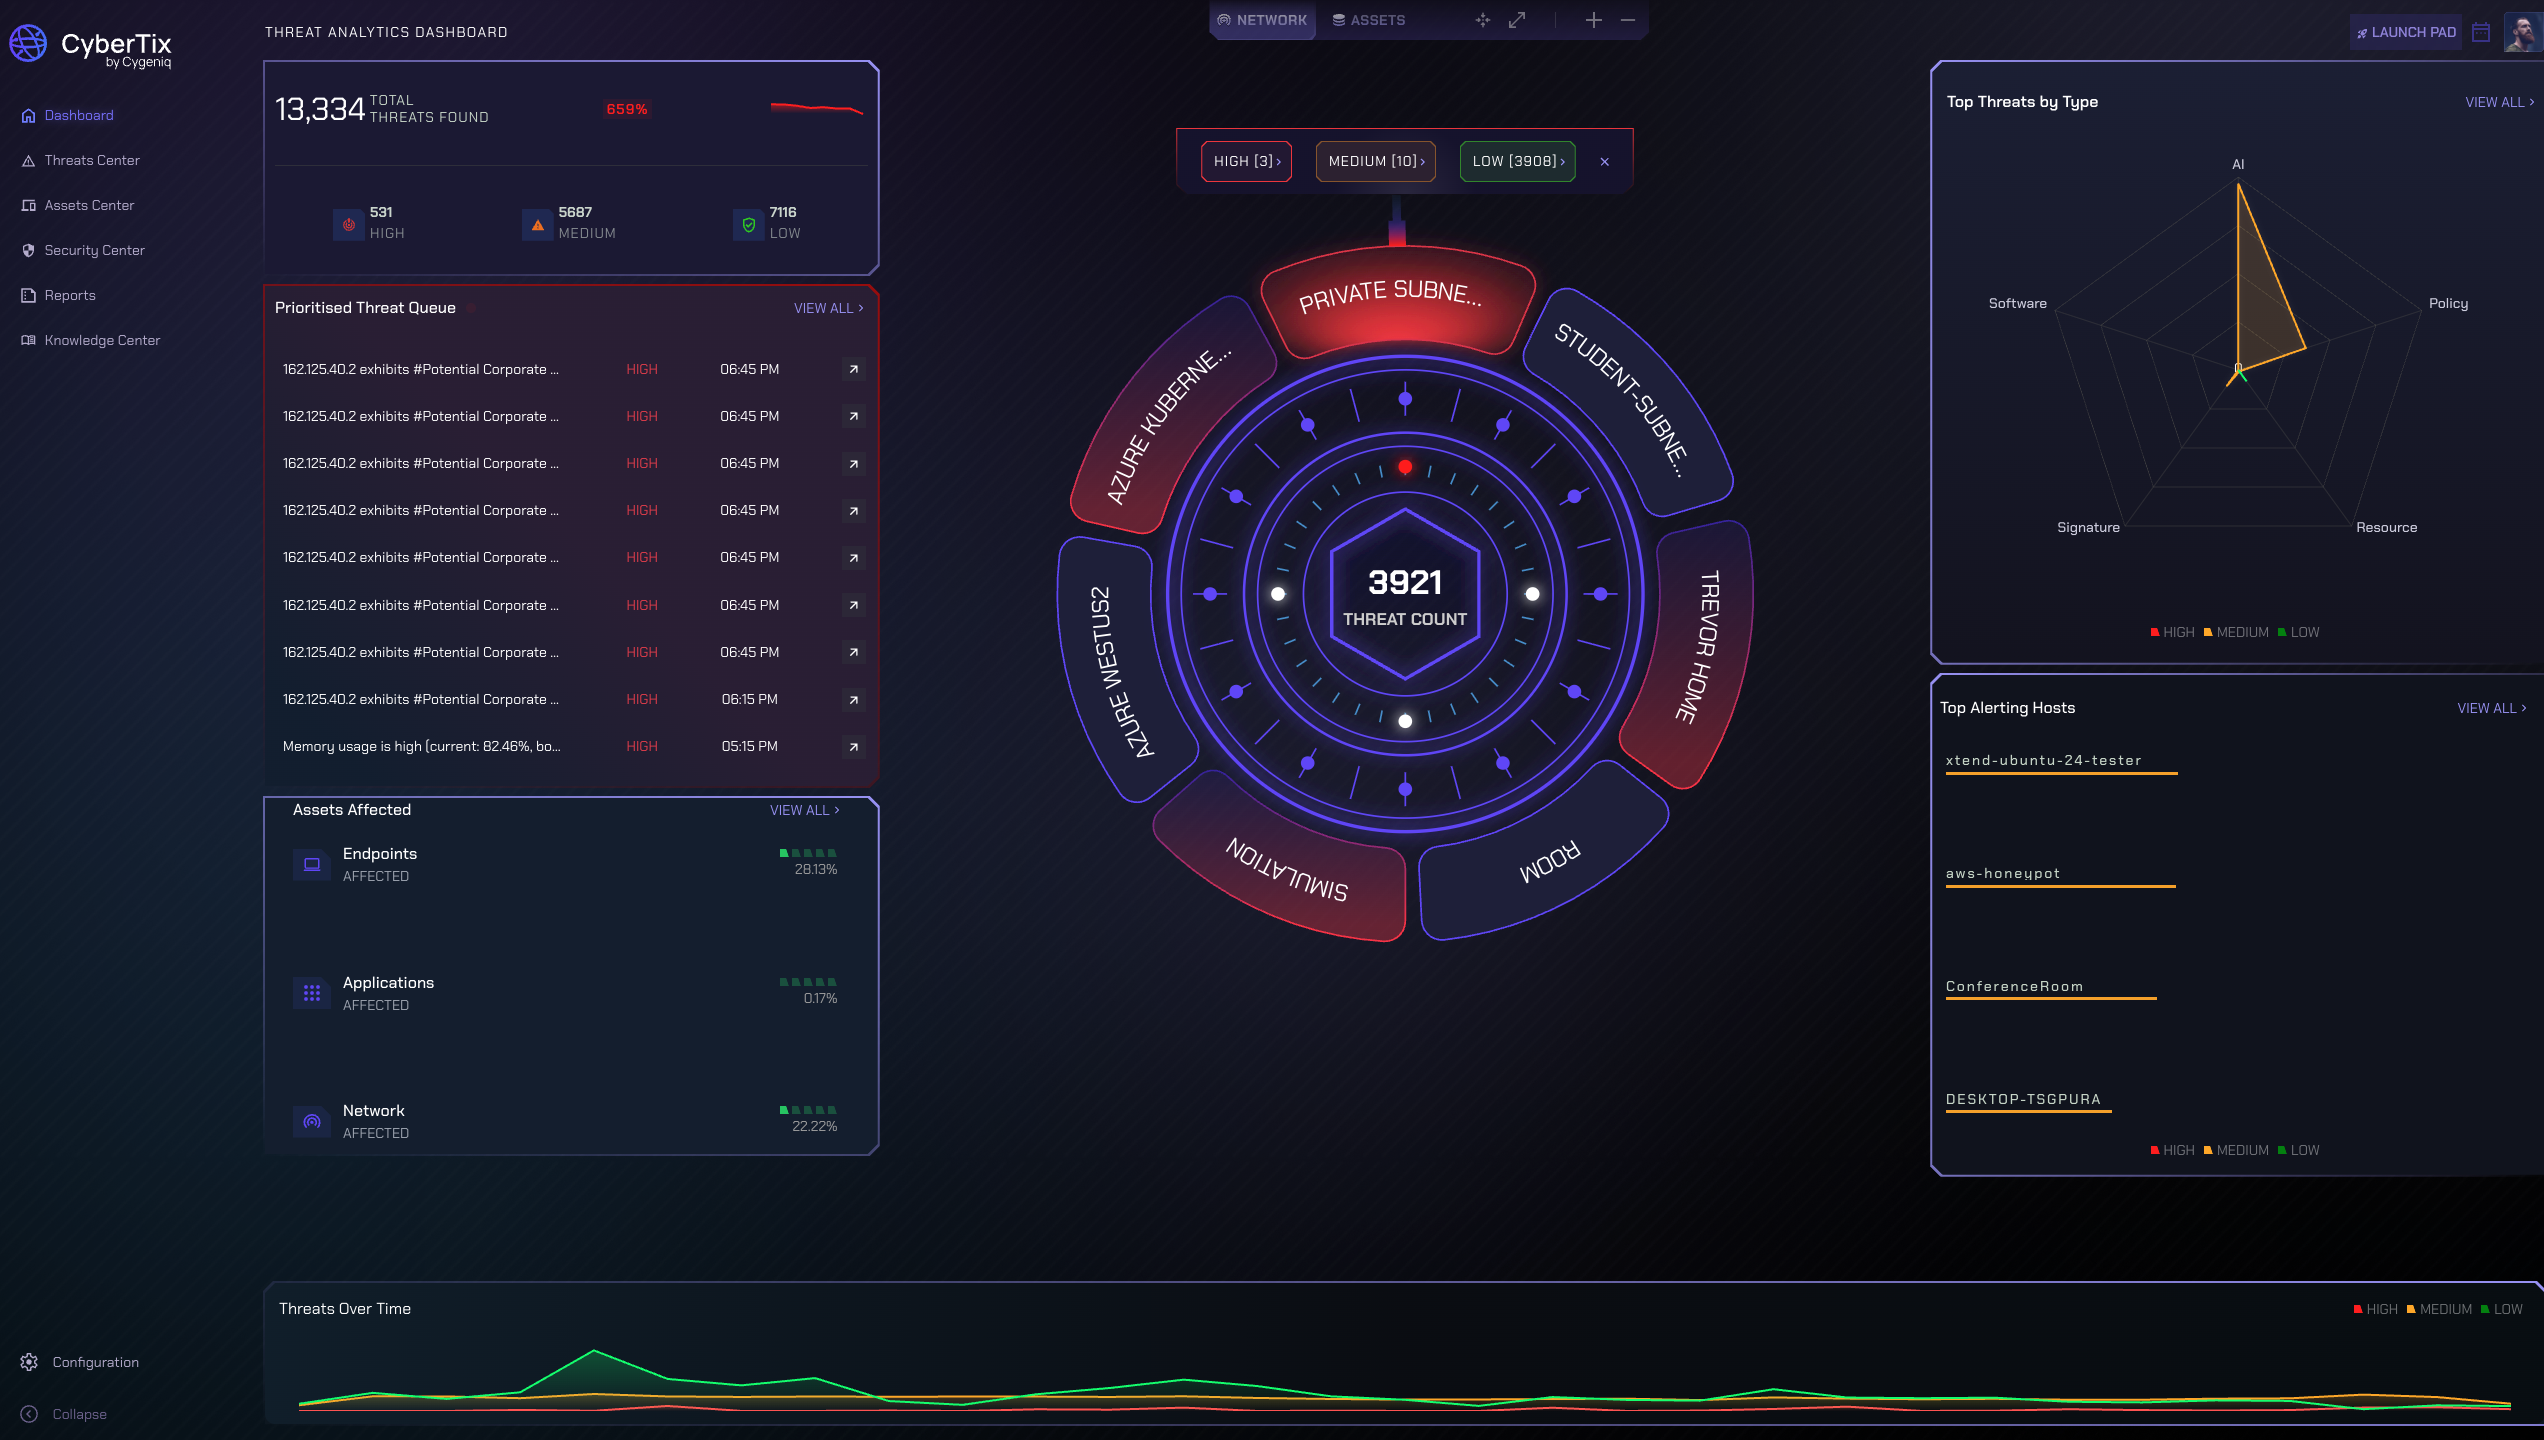
The AI runtime security layer for enterprise AI, on one runtime backbone
CyberTix AI combines LLM security, RAG security, agentic AI security, AI Security Posture Management (AI-SPM), prompt injection protection and AI threat detection and response on one runtime backbone.
AI reshapes security from two directions, and CyberTix AI covers both. CyberTix Secure discovers every LLM, RAG pipeline and autonomous agent you run, protects them inline against AI-native attacks, and detects and contains threats in real time. CyberTix Defend protects the enterprise from AI-powered attacks including AI phishing and BEC, deepfake social engineering, AI-authored malware and autonomous intrusions. Shared telemetry, the same SOC integrations and one AI-risk picture help the business adopt AI aggressively while keeping risk measurable and contained.
Two Directions of AI-Native Risk: Secure Enterprise AI and Defend Against AI-Powered Attacks
AI created an attack surface your controls cannot see and gave attackers a weapon your controls cannot recognize
Attacks on the AI you build break three assumptions classical security depends on: instruction equals data, the model acts on untrusted input, and agents hold real privileges. The model cannot tell your system prompt from text a document slips in. RAG deliberately feeds external content into it. One injection can escalate from a wrong answer to exfiltrated data. To a WAF a prompt-injection payload is just a POST body. To DLP an agent forwarding a confidential file looks like sanctioned app behavior. Attacks powered by AI come from the other direction: adversaries now use generative and agentic AI to attack at a scale, speed and quality no human team could match.
Attacks on the AI You Build
Your firewall/WAF misses prompt injection in a normal API call. DLP misses data leaked through a model answer. The secure web gateway misses a poisoned document in your RAG store. EDR misses an agent misusing a legitimate tool.
AI Phishing and BEC
Flawless, personalized lures at industrial scale, with no human tells.
Deepfake Social Engineering
Cloned voices and live video impersonate executives to authorize fraud.
AI and Polymorphic Malware
LLM-authored, self-mutating code evades signatures.
Autonomous Attacks
Agent-driven recon, exploitation and lateral movement happen at machine speed.
The evidence: 97% attack success from 5 poisoned documents in a 2.68M-document RAG corpus (PoisonedRAG, USENIX 2025). $25M lost to a single deepfake video-call fraud (Arup). $40B projected US GenAI fraud by 2027 (Deloitte). 4× projected growth in major GenAI security incidents by 2029 (Gartner).
AI Runtime Security Capabilities Across CyberTix Secure and CyberTix Defend
Two product lines, 27 capabilities, one platform. CyberTix Secure wraps every AI app you run in a Discover, Protect, Detect, Govern, Assure loop with 15 capabilities. CyberTix Defend protects the enterprise from AI-weaponized attackers across Detect, Protect, Respond, Fortify with 12 capabilities. One runtime backbone, shared telemetry, the same SOC integrations and one AI-risk picture.
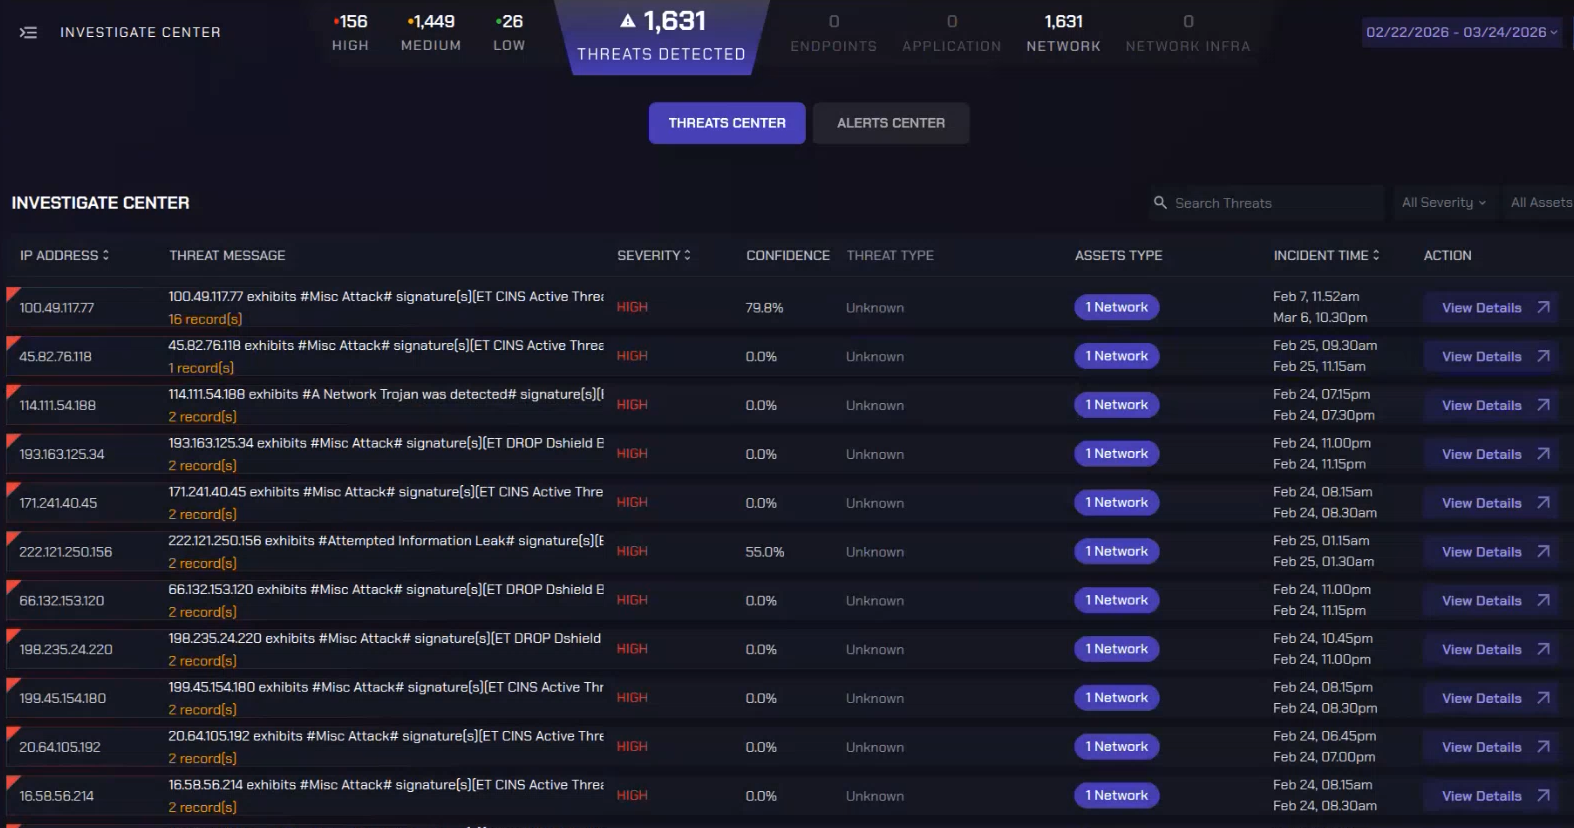
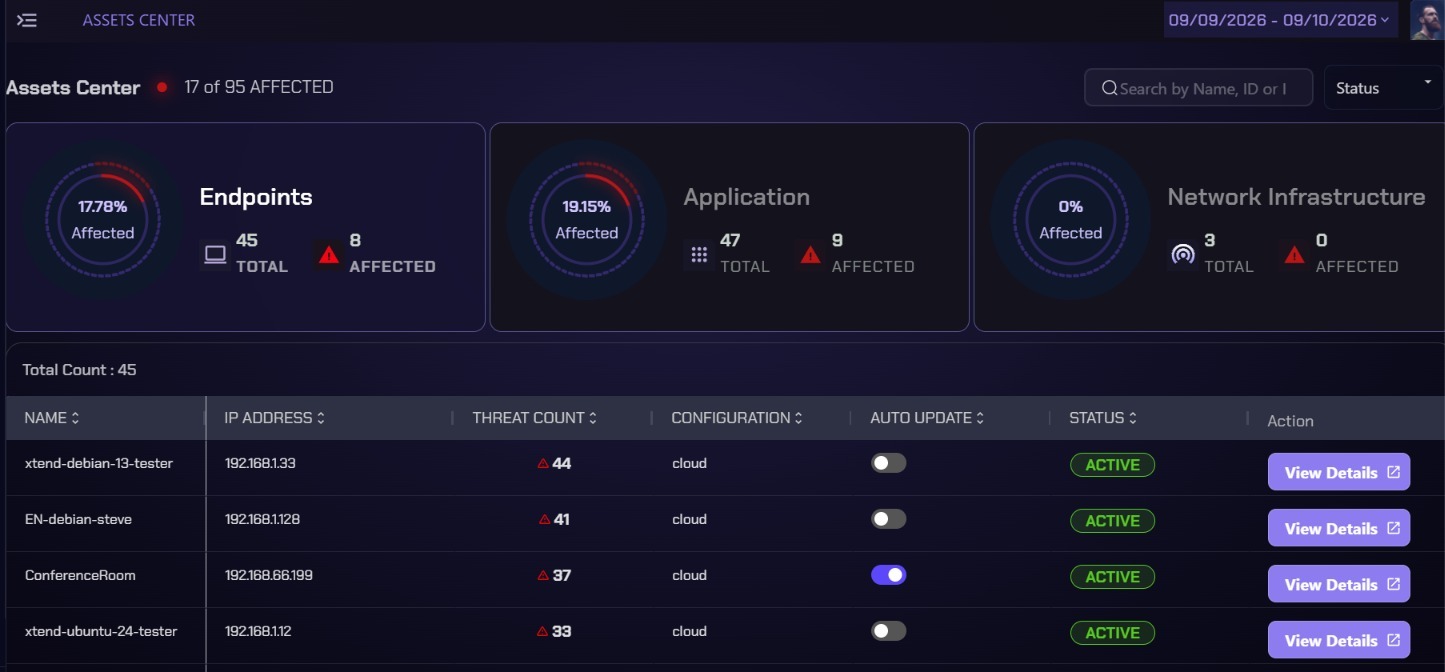
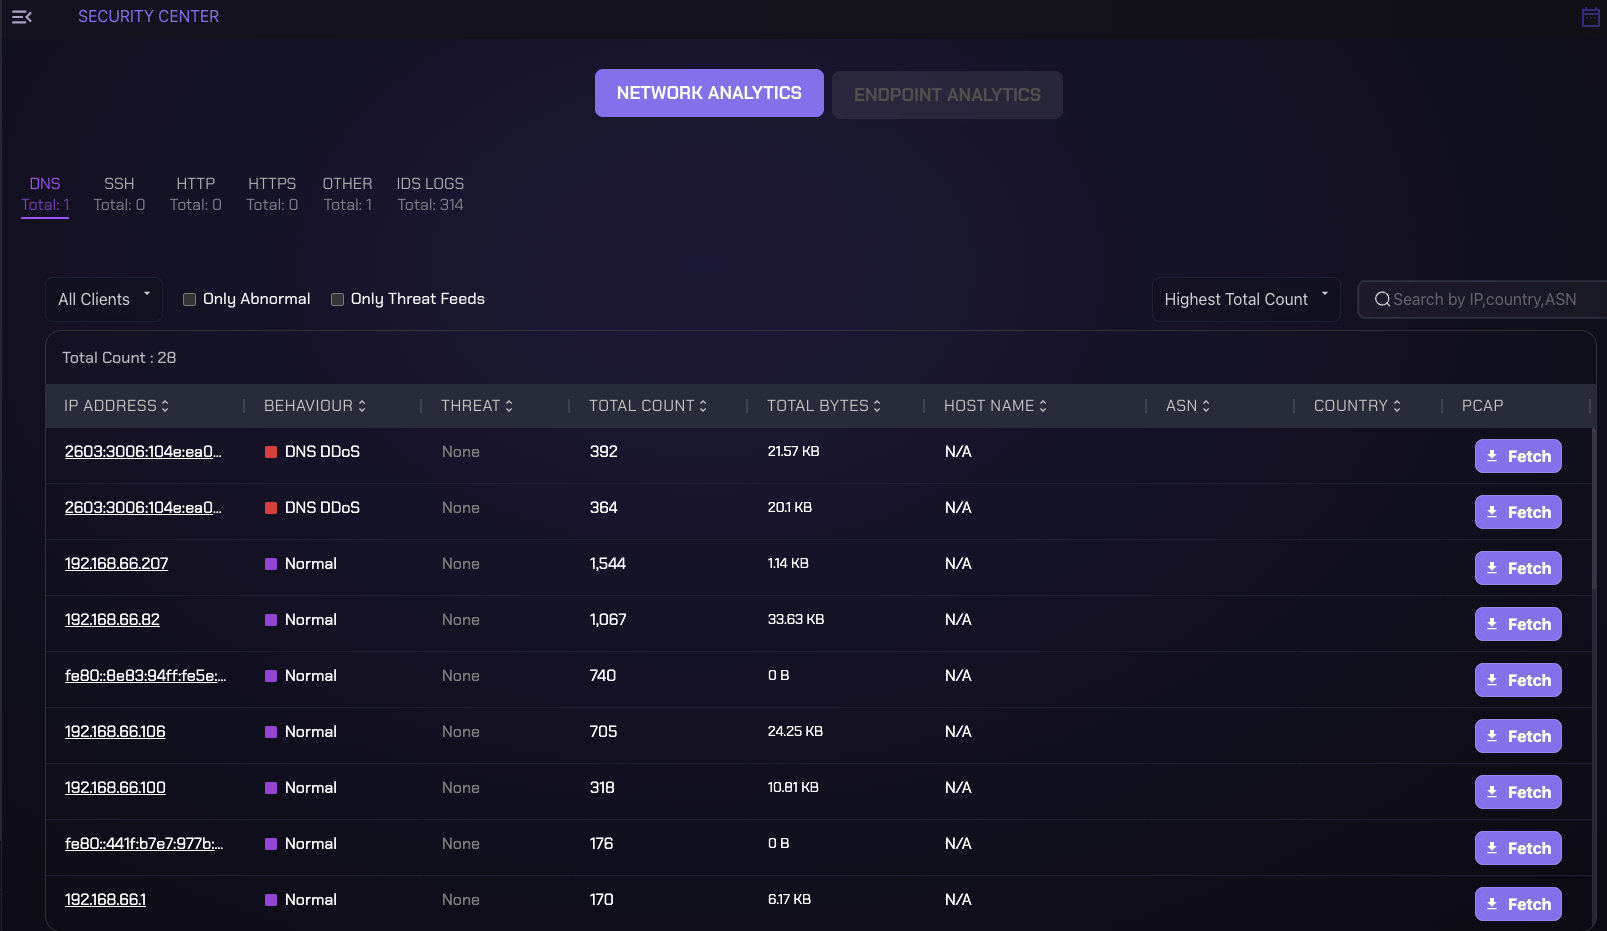
CyberTix Secure: Secure the AI You Build
15 capabilitiesDiscover
See every AI you run, including shadow AI: AI Attack Surface Discovery (Surface), AI Security Posture Management (AI-SPM) with a continuous, trending risk score for every AI asset (Posture), and an AI Bill of Materials and Supply-Chain Map covering every model, dataset and plugin (Lineage).
Protect
Stop AI-native attacks inline, in real time: Prompt Injection and Jailbreak Firewall (Shield), Sensitive Data and Egress Guard for PII, secrets and IP (DataGuard), RAG Integrity and Retrieval Guard that keeps the knowledge base honest and access-controlled (Trust), Agent Action Firewall and Tool Governance (Govern), Non-Human Identity and Access Control with least privilege for every agent and model identity (Identity), and Model Abuse and Cost Protection against denial-of-wallet, DoS and model theft (Meter).
Detect
See attacks unfold and contain them fast: AI Threat Detection and Behavioral Analytics across prompts, data and actions (Detect), AI-Native Telemetry and a tamper-evident Audit Trail of every AI interaction (Trace), and Incident Response and Automated Containment in seconds, not hours (Respond).
Govern
Test continuously and enforce everywhere: Continuous AI Red-Teaming that attacks your own systems before adversaries do (Probe, powered by Hexashield AI), and a Policy Engine and Guardrail Library you author once and enforce across LLM, RAG and agent layers (Policy).
Assure
Prove it with Compliance and Assurance Reporting that provides continuous, audit-ready evidence for AI governance (Comply, powered by GRCortex AI).
CyberTix Defend: Defend Against AI-Weaponized Attackers
12 capabilitiesDetect
See AI-weaponized attacks as they happen: deepfake voice and video detection (Verity), autonomous machine-speed attack detection (Hunter), brand, domain and executive impersonation monitoring (Sentinel), and AI-augmented detection and correlation across every vector (Cortex).
Protect
Stop them before loss: AI-phishing and BEC defense (MailShield), AI-generated and polymorphic malware detection (MalGuard), AI-accelerated exploit shielding (ShieldX), and AI credential and account-takeover defense (IdentityGuard).
Respond
Contain autonomously, under human control: autonomous containment of confirmed incidents with every action logged and explained (Respond).
Fortify
Stay ahead as attackers adopt AI: adversarial-evasion resistance (Resolve), attacker-AI threat intelligence (Recon), and AI attack simulation to prove and improve readiness (Wargame).
OWASP coverage: every class in the OWASP Top 10 for LLM Applications (2025) maps to a named Secure capability. LLM01 Prompt Injection: Shield. LLM02 Sensitive Information Disclosure: DataGuard. LLM03 Supply Chain: Lineage. LLM04 Data and Model Poisoning and LLM08 Vector and Embedding Weaknesses: Trust. LLM06 Excessive Agency: Govern. LLM10 Unbounded Consumption: Meter.
See CyberTix AI Run Against Your Highest-Risk AI Applications
Scope a 90-day pilot: inventory every AI and baseline posture, put inline protection on production apps, and run a first red-team cycle with clear exit criteria.
How CyberTix AI Delivers AI Runtime Security and AI Threat Response
Discover
See every AI you run. Inventory every LLM, RAG pipeline and agent, including shadow AI, and baseline its posture with CyberTix Secure.
Protect
Block attacks inline: prompt injection, jailbreaks, data egress, poisoned retrieval and agent tool abuse on your AI with Secure. Stop AI phishing and BEC, AI malware, exploits and account takeover against your enterprise with Defend.
Detect and Contain
Use behavioral analytics across prompts, data and actions, plus deepfake, impersonation and autonomous-attack detection. Correlate signals into explained incidents and autonomously contain confirmed threats in seconds under human control.
Govern, Assure and Fortify
Use continuous red-teaming and one policy plane, audit-ready evidence, attacker-AI threat intelligence, evasion resistance and attack simulation to prove readiness improves.
Deployment: CyberTix AI deploys inline where enforcement matters and out-of-band where visibility matters. Both lines stream AI-semantic telemetry to your SIEM and SOAR and work with existing IAM and non-human identity, DLP, CI/CD and model gateways or MCP. It extends the SOC. It does not replace it.
CyberTix AI Runtime Security vs Point Tools and Legacy Controls
| Capability | CyberTix AI | Point Tools and Legacy Controls |
|---|---|---|
| Coverage | Attacks on the AI you build and attacks powered by AI: one platform, one AI-risk picture | One layer (prompt, model or agent) or one vector (inbox, endpoint, synthetic media) |
| Enforcement | Inline block on live prompts, retrievals, tool calls and MCP traffic, plus autonomous containment of AI-attack incidents | Static scans, alerts after the fact, or policies on paper |
| Deployment | Monitor-first, then enforce. Layers onto SIEM and SOAR, IAM and DLP | Requires new tooling or a rip and replace |
| Agent control | Action-level control on tool calls plus non-human identity | Not designed for autonomous agents |
| Standards | OWASP LLM Top 10, NIST AI RMF and MITRE ATLAS built in | Ad hoc, or documented but not enforced |
Why AI Runtime Security Matters Now
The attacks legacy tools miss are already working.
Independent research and recent incidents point the same direction: RAG systems can be compromised with a small number of poisoned documents, deepfake fraud has already cost real companies dearly in a single call, and analysts expect AI-generated phishing and fraud to keep climbing. Adoption is ahead of controls, incidents compound from a low base, attackers are already using AI, and the category is forming now. Early movers set the bar.
97% attack success from just 5 poisoned documents in a 2.68M-document corpus (PoisonedRAG, USENIX 2025).
$25M lost to a single deepfake video-call fraud at Arup.
$40B projected US GenAI fraud by 2027 (Deloitte). A 46% rise in AI-generated phishing (Microsoft).
5 to 10 times faster investigations and 30 to 60% less alert noise, measured across Cygeniq deployments.
What Teams Buy CyberTix AI To Do
Secure our RAG chatbot
Ship a knowledge assistant that cannot be poisoned or made to leak.
Safely deploy agents
Let autonomous agents take real actions with guardrails and a kill-switch.
Find and kill shadow AI
Inventory every AI in the organization and shut down what is ungoverned.
Pass the AI audit
Continuous evidence for the NIST AI RMF, the EU AI Act and OWASP.
Stop AI-crafted phishing and payment fraud
Reduced fraud and financial loss.
Prevent deepfake executive and vendor fraud
Brand and executive protection.
Catch autonomous, machine-speed intrusions
Faster detection and response.
Keep defenses effective as attackers adopt AI
Cyber resilience and measurable readiness.
Why CyberTix AI Wins: Built for AI Runtime, Not Retrofitted
Runtime-native
Sees live prompts, retrievals, tool calls and MCP traffic, not just static scans.
Whole-pipeline RAG defense
Guards ingestion, the vector store and retrieval, not only the prompt.
Action-level agent control
Enforces on the agent's tool calls, where the real blast radius lives.
Every AI-attack vector
Email, voice and video, malware, identity and autonomous intrusion in one picture, not one vector at a time.
One policy plane and one backbone
Author guardrails once, with shared telemetry and the same SIEM and SOAR integrations across both lines.
Independent and standards-aligned
Stack-neutral, layers onto any cloud, model or SOC, with OWASP LLM Top 10, NIST AI RMF and MITRE ATLAS built in.
The dual-mandate advantage
One platform to secure the AI you build and defend against the AI used against you, creating a single AI-risk picture no point vendor offers.
Prove Value in 90 Days
Discover
Inventory all AI, baseline posture, find shadow AI and the top risks.
Protect
Inline protection on 2 to 3 production AI apps and a first red-team cycle.
Prove
Demonstrate blocked attacks, risk reduction and SIEM integration, with a scoped pilot and clear exit criteria before enterprise-wide rollout.
Start out-of-band: deploy in monitor mode first, with full visibility and zero disruption to AI apps.
Tune, then enforce: move from monitor to block once policies are validated against real traffic.
Frequently Asked Questions
What is AI runtime security?
AI runtime security protects AI systems while they are operating, not only before deployment. CyberTix AI monitors and enforces controls across live prompts, retrievals, tool calls, agent actions and AI-semantic telemetry, while also detecting and responding to AI-powered attacks against the wider enterprise.
What is the difference between CyberTix Secure and CyberTix Defend?
They cover the two directions of AI-native risk. CyberTix Secure protects the AI you build, including LLMs, RAG pipelines and agents, against prompt injection, RAG poisoning, agent abuse, data egress and model theft. It provides 15 capabilities across Discover, Protect, Detect, Govern and Assure. CyberTix Defend protects the enterprise against attackers who use AI, including AI phishing and BEC, deepfakes, AI-authored malware and autonomous intrusions. It provides 12 capabilities across Detect, Protect, Respond and Fortify. They share one runtime backbone, one telemetry stream and the same SOC integrations, so you get one AI-risk picture.
Does CyberTix Secure protect RAG pipelines and agents, or just prompts?
All three layers. A prompt-injection filter on its own is not AI security. CyberTix Secure guards the whole RAG pipeline, including ingestion, the vector store and retrieval, and enforces on the agent actual tool calls with least-privilege identity for every agent and model, because that is where the real blast radius lives.
How is CyberTix AI deployed?
Monitor-first. CyberTix AI starts out-of-band for full visibility with zero disruption, then moves from monitor to block once policies are validated against real traffic. It deploys inline where enforcement matters, streams AI-semantic telemetry to your SIEM and SOAR, and works with existing IAM, DLP, CI/CD and model gateways or MCP. Nothing is replaced.
Can CyberTix Defend detect deepfake voice and video?
Yes. Verity detects cloned voices and synthetic video used to impersonate executives and vendors, and Sentinel monitors brand, domain and executive impersonation. Unlike single-vector deepfake tools, CyberTix Defend correlates those signals with email, identity and endpoint telemetry in one incident, so a deepfake call and the payment request that follows it are seen together.
Does CyberTix AI replace SIEM or SOAR?
No. CyberTix AI extends the SOC. It streams AI-semantic telemetry into existing SIEM and SOAR and works with IAM, non-human identity, DLP, CI/CD and model gateways or MCP. It can deploy inline where enforcement matters and out-of-band where visibility matters.
How does CyberTix AI protect against prompt injection and RAG poisoning?
CyberTix Secure uses the Prompt Injection and Jailbreak Firewall (Shield) for inline prompt protection and the RAG Integrity and Retrieval Guard (Trust) to protect ingestion, the vector store and retrieval. It also combines data egress controls, agent tool governance, non-human identity and runtime detection so protection is not limited to the prompt layer.
Adopt AI Aggressively. Keep the Risk Measurable and Contained
Let us scope a 90-day pilot on your highest-risk AI applications and attack vectors: inventory every AI and baseline posture in weeks 0 to 4, inline protection on 2 to 3 production apps and a first red-team cycle by week 12, then blocked attacks, risk reduction and SIEM integration demonstrated, with clear exit criteria before enterprise-wide rollout.
