GRCortex AI: AI Governance Platform for Continuous Risk and Compliance
Continuous AI governance, risk and compliance, mapped once and kept audit-ready.
Part of the Cygeniq Runtime AI Trust Platform: Govern your AI.
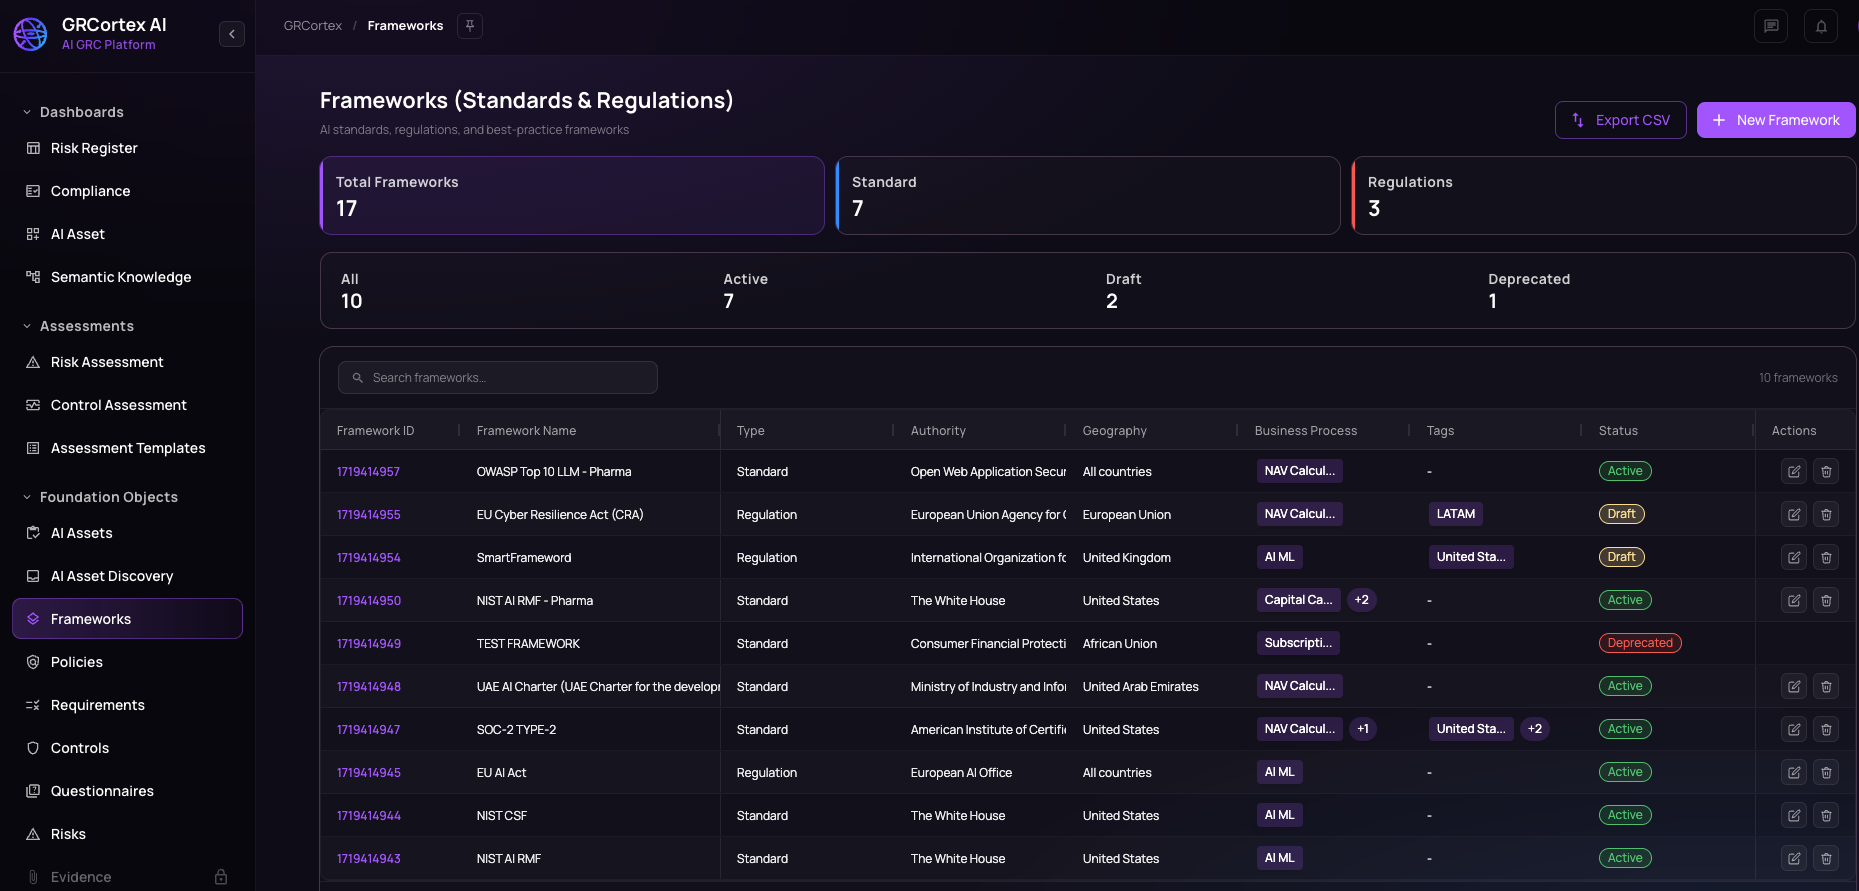
Cygeniq's AI governance platform for regulated enterprises
GRCortex AI provides AI governance, risk and compliance in one connected system, combining AI asset discovery, an AI risk register, cross-framework control mapping, continuous control monitoring, and audit evidence.
Controls can be reused across supported frameworks such as the EU AI Act, NIS2, NIST AI RMF, ISO/IEC 42001 and IEC 62443, while requirement-specific gaps are identified and evidence remains traceable for review. This helps turn continuous AI compliance into an operating process rather than a point-in-time audit exercise.
Why Traditional GRC Creates an AI Governance and Compliance Gap
AI governance becomes harder to manage as regulations, standards, and assurance requirements multiplies
AI programs may need to address different types of requirements and guidance, for example, the EU AI Act as a regulation, NIST AI RMF as voluntary risk-management guidance, ISO/IEC 42001 as an AI management-system standard, and assurance frameworks such as SOC 2. Each has its own scope, requirements, implementation expectations, and evidence considerations.
Traditional GRC can lead to repeated mapping, framework-specific gap analysis, and manual evidence collection. As AI systems and controls change, that evidence can quickly become stale.
GRCortex AI provides a shared control layer across supported frameworks, helping teams reuse controls, identify requirement-specific gaps, and maintain traceable evidence for review.
Framework Silos
Each new regulation gets its own spreadsheet, even when the underlying controls barely change.
Evidence Assembled by Hand
Audit packs get built the week before they are due, then age out immediately.
No Runtime Link
Governance describes what a model should do. It rarely reflects what a model is actually doing in production.
AI Governance, Risk Management and Compliance Capabilities
Whether you call it AI governance software, an AI GRC platform or an AI compliance platform, the job is the same: prove what your AI systems are doing, continuously.
AI Asset Discovery and BOM
Every model, agent and use case is tracked with an owner and a risk tier, not a spreadsheet someone forgot to update.
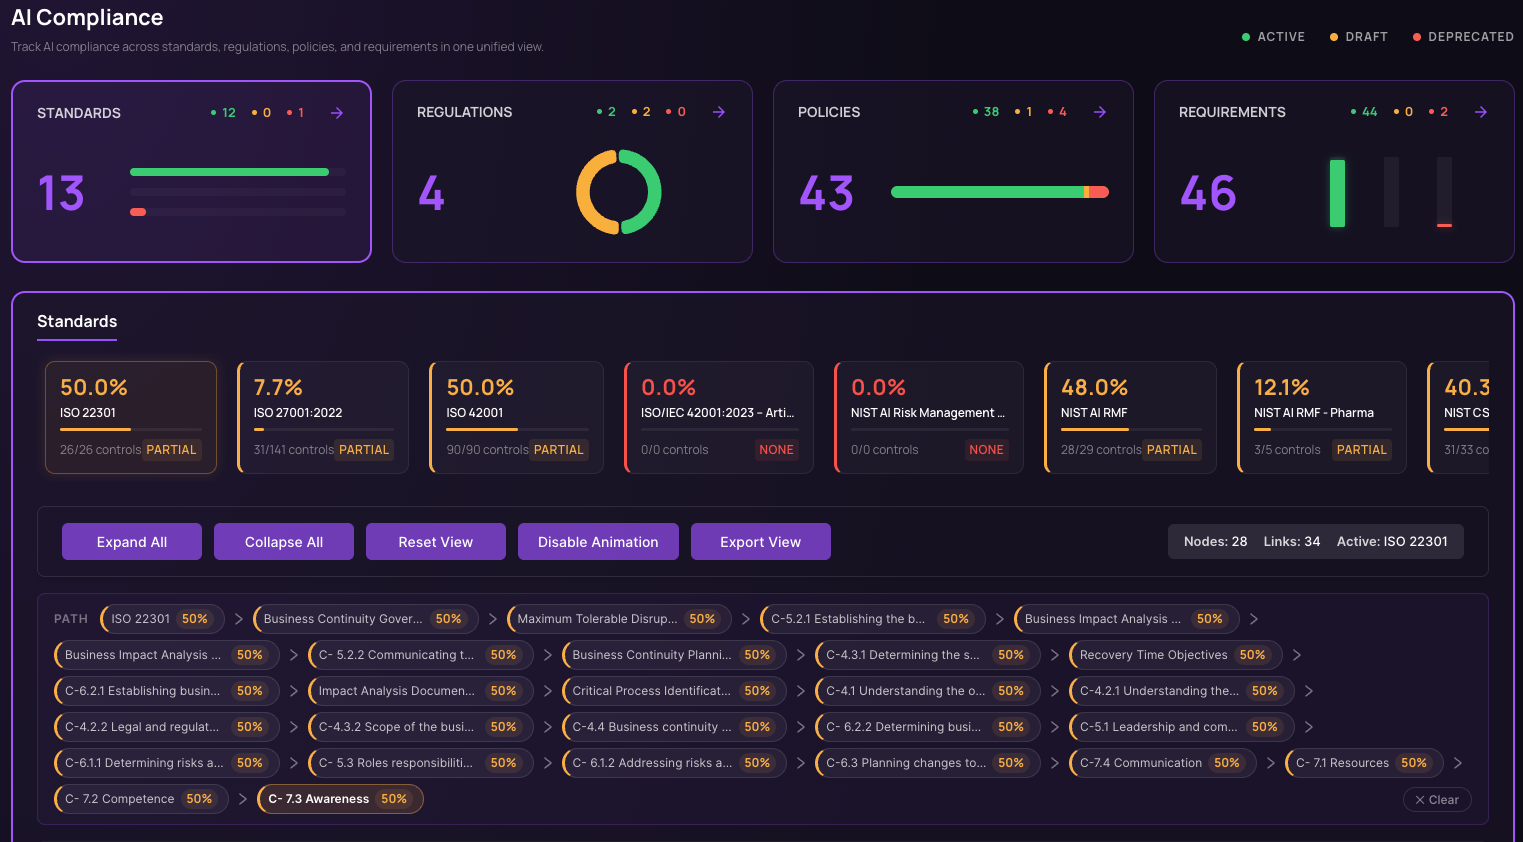
Cross-Framework Unified Control Framework (UCF)
EU AI Act, NIST AI RMF, ISO, NYDFS and HIPAA are mapped once against a shared control framework, not rebuilt per regulation.
Automated Policy-to-Control Mapping
Policy, control and evaluation are connected automatically as your AI estate changes.
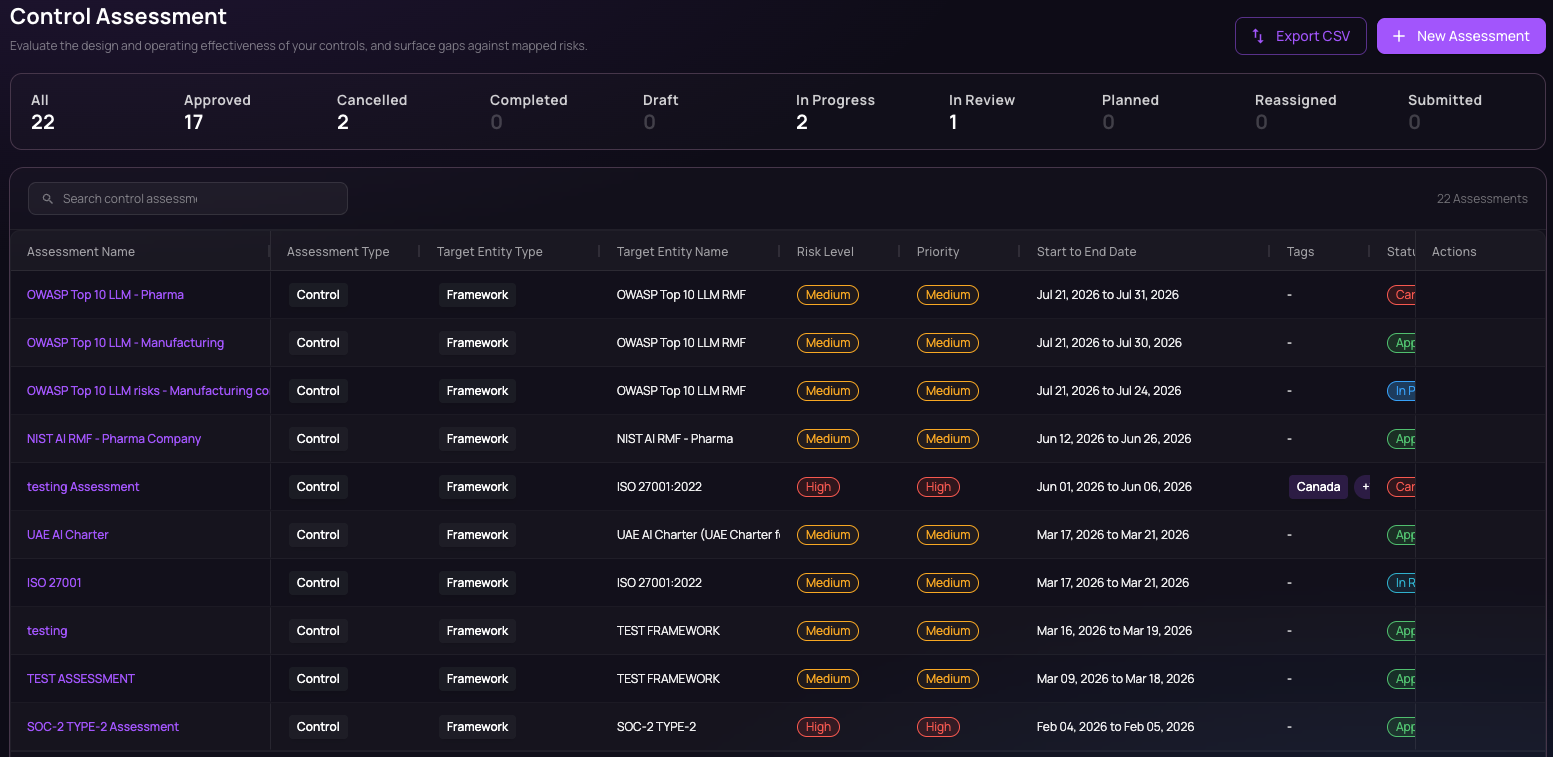
Continuous Control Monitoring
Live control effectiveness and remediation tracking replace a once-a-year check.
Automated Regulatory Mapping
EU AI Act, NIS2, ISO/IEC 42001, NIST AI RMF, IEC 62443, SOC 2, UAE, UK and emerging AI regulation are kept current as the rules change.
Audit-Ready Reporting
AI audit evidence packs and board risk views are generated on demand, not assembled the week before an audit.
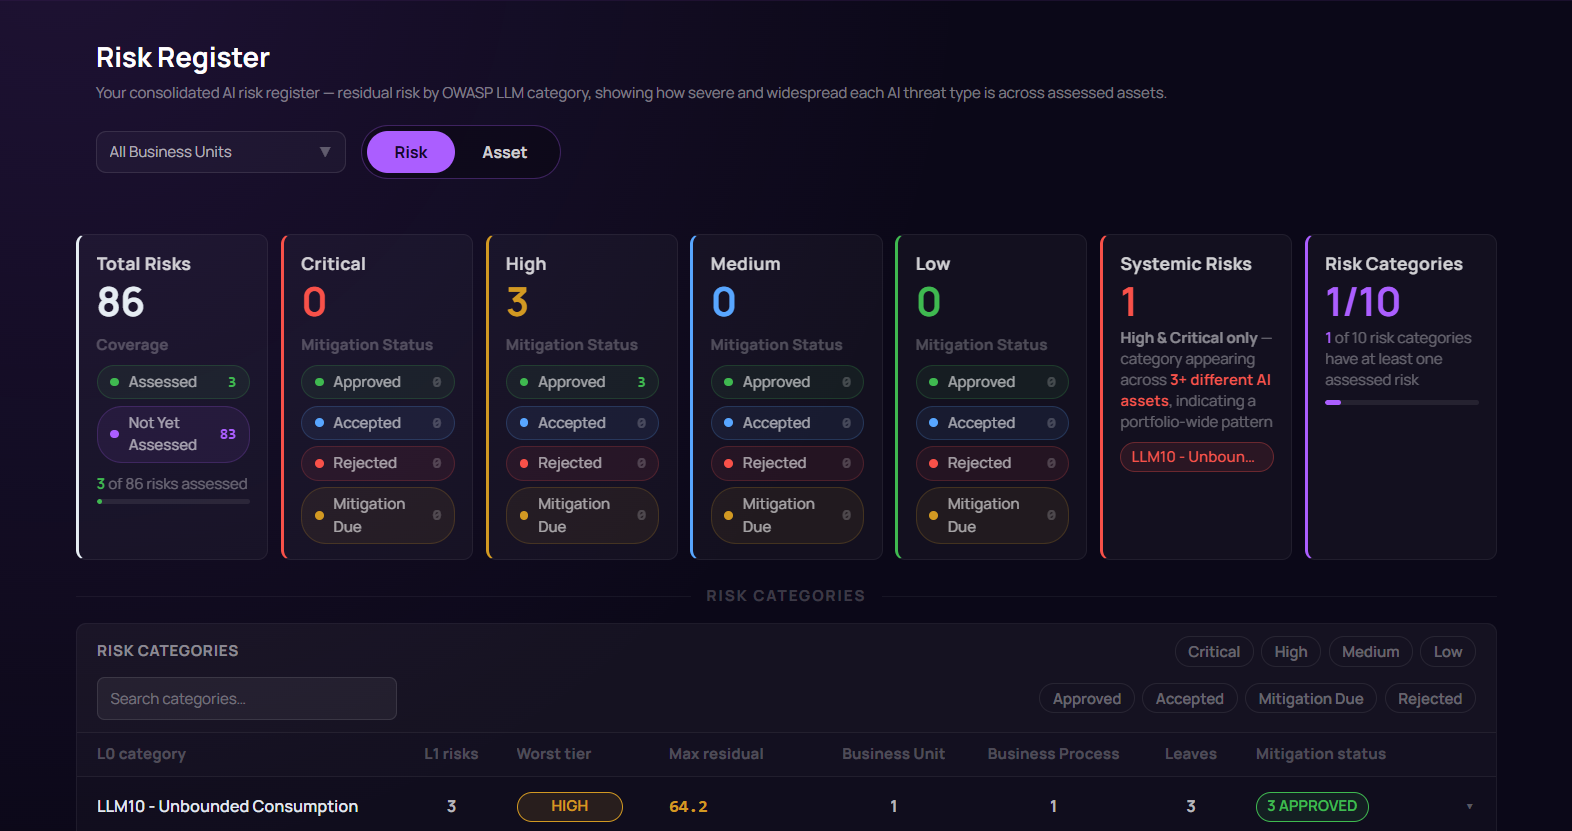
Dynamic AI Risk Register
Every AI system carries a live risk tier fed by Hexashield AI red-team and runtime findings and CyberTix AI incidents, so the register reflects what is running today.
Fed by Hexashield AI and CyberTix AIBoard-Ready AI Assurance
Executive dashboards, the organization-wide AI Trust Score and three lines of defense (3LoD) reporting provide board-ready assurance.
See GRCortex AI Mapped to the Frameworks You Already Report Against
Book a walkthrough of asset discovery, cross-framework mapping, continuous monitoring and audit-ready evidence, shown against your regulations.
How GRCortex AI Automates AI Governance and Continuous Compliance
Discover Your AI Estate
Connect models, agents and use cases, and map each to an owner and a risk tier automatically.
Map Controls Once
Apply a shared control framework across EU AI Act, NIST AI RMF, ISO, NYDFS and HIPAA instead of rebuilding per regulation.
Monitor Continuously
Track control effectiveness and remediation status as your AI systems change, not just at audit time.
Generate Evidence on Demand
Produce audit-ready evidence packs and board risk views whenever they are needed, already current.
Frameworks covered: EU AI Act, NIS2, NIST AI RMF, ISO/IEC 42001, IEC 62443, SOC 2, NYDFS, HIPAA, and UAE and UK AI regulation, mapped once through a shared control framework.
Continuous AI Governance vs Manual Framework-by-Framework GRC
| Capability | GRCortex AI | Manual, Framework-by-Framework |
|---|---|---|
| Framework mapping | Mapped once across every framework | Rebuilt separately for each regulation |
| Control monitoring | Continuous, live effectiveness tracking | Checked at audit time only |
| Evidence | Generated automatically, always current | Assembled by hand before each audit |
| Regulatory updates | Mapped automatically as rules change | Manually tracked and re-mapped |
| Runtime visibility | Reconciled against what models actually do | Disconnected from runtime behavior |
Results from a Tier One Bank
A tier one bank brought GRCortex AI in to cover its AI systems across several overlapping regulatory frameworks at once. The governance team no longer rebuilds the same controls for every new regulation, and the evidence they hand to regulators reflects what is currently running instead of a report assembled the previous quarter, cutting audit preparation effort by 80 to 90%.
80 to 90% less audit preparation effortmeasured after adopting GRCortex AI across overlapping frameworksFrequently Asked Questions
What is an AI governance platform?
An AI governance platform is software that tracks an organization's AI systems, maps them to regulatory and internal controls, and keeps evidence of compliance current as those systems change. Instead of treating governance as a document written once before launch, it treats governance as something that has to stay accurate while models, agents and data keep changing.
How do you automate AI compliance evidence?
AI compliance evidence gets automated by connecting directly to the systems it describes. Asset inventories, control mappings and monitoring data feed into evidence packs automatically instead of being assembled by hand. When a regulator or an auditor asks for proof, the evidence reflects the current state of the system, not a snapshot from months earlier.
How do you maintain an AI risk register?
An AI risk register stays current by linking each entry to a live asset instead of a static description, which is why an AI risk management platform has to track that link automatically. As a model, agent or use case changes, its risk tier, control status and mitigation record update with it, so the register reflects what is actually running rather than what was true when it was first assessed.
How does GRCortex AI connect governance to what AI systems are actually doing?
GRCortex AI consumes live findings from Hexashield AI, including red-team results, guardrail events and drift, and CyberTix AI incidents. A red-team finding becomes a compliance exception and a board metric automatically, and a compliance gap can tighten a guardrail. This creates the closed loop a standalone GRC platform cannot provide.
What is continuous AI compliance?
Continuous AI compliance keeps controls, risk status and evidence current as AI systems change. GRCortex AI continuously monitors control effectiveness, maps regulatory requirements through a shared control framework and generates current evidence on demand rather than rebuilding it at audit time.
How does GRCortex AI support EU AI Act compliance and ISO 42001 compliance?
GRCortex AI maps controls once across frameworks including the EU AI Act and ISO/IEC 42001, monitors control effectiveness continuously and generates audit-ready evidence from the current AI estate. The same shared control framework also supports NIS2, NIST AI RMF, IEC 62443, SOC 2, NYDFS, HIPAA and other listed regulations.
What is AI audit evidence?
AI audit evidence is the current record that supports how an AI system is governed, including asset ownership, risk tier, control mappings, monitoring status and related runtime findings. GRCortex AI generates these evidence packs on demand instead of assembling screenshots and spreadsheets before an audit.
See Where Your AI Governance Has Gaps Before Your Next Audit Does
Book a walkthrough of GRCortex AI: asset discovery, cross-framework mapping, continuous monitoring and audit-ready evidence, shown against frameworks you already report against.
